# A call for collective action on cyber defense
**作者**: Greg Brockman
**日期**: 2026-08-27T17:03:19.000Z
**来源**: [https://x.com/gdb/status/2093021551855812842](https://x.com/gdb/status/2093021551855812842)
---
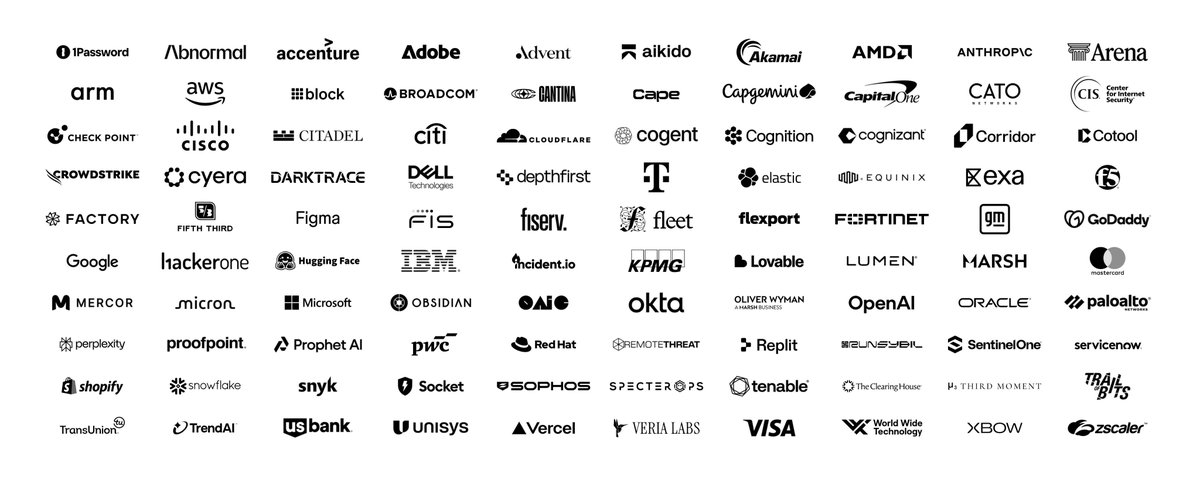
An open letter for a global surge in cyber defense, signed by over 100 organizations including Anthropic, AWS, Google, Microsoft, OpenAI, and Oracle.
We have a limited window to strengthen cyber defenses.
In the coming months, AI-enabled cyber attacks will become far more widespread and sophisticated as models around the world become increasingly capable. The companies and public services our communities depend on — from hospitals to water treatment plants to the infrastructure that powers the internet — are at risk.
Today’s AI advances are already giving defenders new ways to fix weaknesses that have accumulated for years. If we act decisively, we can use the defenders’ window to make our digital world much more secure.
We propose the following principles for a collective response:
- Recognize that status quo security won’t be enough. Longstanding bugs, excessive permissions, misconfigurations, insecure and unpatched software, weak authentication, and technical debt in legacy systems have left systems exposed. Security teams, particularly for critical infrastructure, have been historically under-resourced and need a surge in tools and resources.
- Empower more defenders with cyber-capable AI. AI brings specialist skills to more defenders and makes core security tasks faster, cheaper and better. Sharing tools, practical knowledge, and verified fixes lets one organization’s work help protect many others.
- Mobilize a collective response. Cyber capabilities are advancing worldwide, and that can be a net positive: no single company should control the future. It also means a global response is necessary, requiring new partnerships to raise security standards and find new solutions to emerging cyber threats.
Each of us can reduce risk now. All organizations, cybersecurity companies, technology partners, governments, and AI frontier companies have an important role: accelerate defenders’ priorities with tools, funding, and hands-on support, especially for critical infrastructure organizations with limited budgets.
Here’s what we think needs to happen next:
## 01 Every organization
Make cyber defense an immediate leadership priority. Raise your security standards and meet them with the urgency and coordination of an incident that takes precedence over everything except critical business operations. Fix the highest-risk weaknesses, verify results without disrupting essential services, and raise the security bar for what you buy, build, and deploy, including AI-generated code. Upgrade or replace systems to build in least privilege, strong access controls, and defense in depth. Use capable, lower-cost models for broad coverage, and apply frontier capabilities to the hardest problems. Where a system cannot be patched without disrupting essential services, apply and verify compensating controls.
## 02 Cybersecurity companies and technology partners
Help lead the response to defend against sustained AI-enabled attacks, including testing defenses continuously against frontier cyber capabilities, strengthening existing tools with AI, and working with technology partners to close gaps now. Make AI-powered defense accessible and deployable for critical-infrastructure operators, with hands-on help to deploy tools and verify fixes, and collaborate with critical infrastructure supply chain manufacturers and system integrators to patch and issue interim guidance. Share threat intelligence and tested playbooks, and measure progress by how many organizations are protected, how quickly attacks are contained, and whether fixes work.
## 03 Governments
Coordinate cyber defense at local, national, and international levels. Strengthen existing government and industry channels to share actionable threat intelligence, prioritize the most serious risks, and coordinate incident response and recovery around the world. Fund cyber defense, starting with essential services that lack the staff or budget to act. Expedite the expansion of trusted access programs, especially for critical infrastructure supply chains, and broaden access to defensive capabilities for other defenders. Give hospitals, water utilities, and local governments access to capable defensive AI, authorized testing, and hands-on support through trusted security providers and partners. Impose costs on attackers.
## 04 Frontier AI companies
Provide responsible model access, significant funding, training, and hands-on support, especially for under-resourced critical-infrastructure defenders. Build observability and security tools, ensure agentic identities are traceable and accountable, and share best practices in continuous monitoring. Invest in authorized testing, private disclosure, and verified fixes, and share tools, playbooks, and credible threat assessments with governments, security partners, and open-source maintainers to strengthen preparedness, response, and recovery.
We can make the digital infrastructure we all depend on more secure.
We call on leaders across industry and government to bring the full weight of their technology, resources, and expertise to this effort. Put cyber-capable AI in the hands of defenders, starting with the teams protecting essential services. Fix the most dangerous weaknesses, verify the fixes, and share what works so others can build on it. Together, we can turn today’s AI advances into lasting improvements in security that benefit everyone. Let’s put them to work.
[https://openai.com/collective-cyberdefense](https://openai.com/collective-cyberdefense)
## 相关链接
- [Greg Brockman](https://x.com/gdb)
- [@gdb](https://x.com/gdb)
- [586K](https://x.com/gdb/status/2093021551855812842/analytics)
- [https://openai.com/collective-cyberdefense](https://openai.com/collective-cyberdefense)
- [Upgrade to Premium](https://x.com/i/premium_sign_up)
- [1:03 AM · Aug 28, 2026](https://x.com/gdb/status/2093021551855812842)
- [586.7K Views](https://x.com/gdb/status/2093021551855812842/analytics)
- [View quotes](https://x.com/gdb/status/2093021551855812842/quotes)
---
*导出时间: 2026/8/28 08:57:05*
---
## 中文翻译
# 呼吁在网络防御领域采取集体行动
**作者**: Greg Brockman
**日期**: 2026-08-27T17:03:19.000Z
**来源**: [https://x.com/gdb/status/2093021551855812842](https://x.com/gdb/status/2093021551855812842)
---

一封呼吁全球大规模加强网络防御的公开信,由包括 Anthropic、AWS、谷歌、微软、OpenAI 和甲骨文在内的 100 多个组织共同签署。
我们拥有一个有限的时间窗口来强化网络防御。
在接下来的几个月里,随着世界各地的人工智能模型能力日益增强,AI 驱动的网络攻击将变得更加普遍和复杂。我们社区赖以运转的公司和公共服务——从医院到水处理厂,再到支撑互联网运行的基础设施——都面临风险。
今天的人工智能进步已经为防御者提供了新的手段,来修复多年积累的漏洞。如果我们果断行动,就能利用这个属于防御者的窗口期,让我们的数字世界安全得多。
我们为集体应对提出以下原则:
- 认识到维持现状的安全措施已远远不够。长期存在的漏洞、过多的权限、配置错误、不安全且未打补丁的软件、薄弱的身份验证,以及遗留系统中的技术债务,都使系统暴露在风险之中。安全团队,尤其是关键基础设施领域的安全团队,历来资源不足,急需工具和资源的大幅补充。
- 用具备网络能力的 AI 赋能更多防御者。AI 能为更多防御者带来专业技能,使核心安全任务更快、更便宜、更高效。共享工具、实用知识和经过验证的修复方案,能让一个组织的成果保护许多其他组织。
- 动员集体响应。网络能力正在全球范围内不断进步,这可以是净收益:不应由任何单一公司掌控未来。这也意味着全球性的应对必不可少,需要建立新的合作伙伴关系,以提升安全标准,并为新出现的网络威胁寻找新的解决方案。
我们每个人现在就能降低风险。所有组织、网络安全公司、技术合作伙伴、政府和前沿 AI 公司都有重要角色:通过工具、资金和实际支持来加速满足防御者的优先需求,尤其是对那些预算有限的关键基础设施组织。
以下是我们认为接下来需要发生的事情:
## 01 每一个组织
将网络防御作为领导层的当务之急。提升你的安全标准,并以处理事故般的紧迫感和协调力度去达成——这种优先级仅次于关键业务运营。修复风险最高的弱点,在不中断关键服务的前提下验证结果,并提高对所采购、构建和部署内容(包括 AI 生成的代码)的安全门槛。升级或替换系统,以内置最小权限、强大的访问控制和纵深防御。使用能力强、成本低的大规模覆盖模型,并将前沿能力应用于最困难的问题。当系统无法在不中断关键服务的情况下打补丁时,应用并验证补偿性控制措施。
## 02 网络安全公司和技术合作伙伴
帮助带头应对持续的 AI 驱动攻击,包括持续针对前沿网络能力测试防御体系、用 AI 强化现有工具,以及与技术合作伙伴合作,立即弥合差距。让 AI 驱动的防御对关键基础设施运营者而言易于获取和部署,并亲身协助部署工具和验证修复方案;与关键基础设施供应链制造商和系统集成商合作打补丁并发布临时指导。共享威胁情报和经过测试的应对手册,并以多少组织受到保护、攻击被遏制得多快、修复方案是否有效来衡量进展。
## 03 政府
在地方、国家和国际层面协调网络防御。加强现有的政府与行业渠道,共享可操作的威胁情报,优先处理最严重的风险,并在全球范围内协调事件响应与恢复。为网络防御提供资金,首先从缺乏人力或预算采取行动的基本服务开始。加快扩展可信访问计划,尤其是针对关键基础设施供应链,并扩大其他防御者获取防御能力的途径。通过可信的安全服务提供商和合作伙伴,让医院、水务公司和地方政府获得能力强大的防御型 AI、授权测试和实际支持。让攻击者付出代价。
## 04 前沿 AI 公司
提供负责任的模型访问、大量资金、培训和实际支持,尤其是面向资源不足的关键基础设施防御者。构建可观测性和安全工具,确保智能体身份可追溯、可问责,并分享持续监控的最佳实践。投资于授权测试、私下披露和经验证的修复方案,并与政府、安全合作伙伴和开源维护者共享工具、应对手册和可信的威胁评估,以增强准备、响应和恢复能力。
我们能够让我们共同依赖的数字基础设施更加安全。
我们呼吁业界和政府的领导者将他们的全部技术、资源和专业能力投入到这项事业中。把具备网络能力的 AI 交到防御者手中,从保护基本服务的团队开始。修复最危险的漏洞,验证修复效果,并分享有效的经验,让其他人得以在此基础上继续推进。齐心协力,我们就能把今天的人工智能进步转化为惠及每个人的持久安全改进。让我们行动起来吧。
[https://openai.com/collective-cyberdefense](https://openai.com/collective-cyberdefense)
## 相关链接
- [Greg Brockman](https://x.com/gdb)
- [@gdb](https://x.com/gdb)
- [586K](https://x.com/gdb/status/2093021551855812842/analytics)
- [https://openai.com/collective-cyberdefense](https://openai.com/collective-cyberdefense)
- [Upgrade to Premium](https://x.com/i/premium_sign_up)
- [1:03 AM · Aug 28, 2026](https://x.com/gdb/status/2093021551855812842)
- [586.7K Views](https://x.com/gdb/status/2093021551855812842/analytics)
- [View quotes](https://x.com/gdb/status/2093021551855812842/quotes)
---
*导出时间: 2026/8/28 08:57:05*